Cybersecurity researcher and embedded hardware specialist
Chris Watts
Chris Watts is an Australian cybersecurity researcher and embedded hardware security specialist. He is a Senior Cybersecurity Consultant at CyberCX, where he leads the embedded hardware testing capability, and he is the researcher credited by Cisco and NetComm for a series of vulnerability reports in cable modems, residential gateways, IP phones, carrier routers and industrial equipment published between 2014 and 2024.
He founded Tech Analysis, the Sydney consultancy under which his earlier research was published, co-founded the landing-page company PageLeap with Will Pemble, and created Wonderland History, a website documenting the Wonderland Sydney amusement park. His career spans more than three decades of programming, network and systems engineering, electronics and security work.
Chris joined CyberCX, an Australian cyber security company, in November 2020. He is a Senior Cybersecurity Consultant in its Security Testing and Assurance practice and the practice's Embedded Systems Service Lead and subject matter expert for embedded systems penetration testing. In that role he leads the embedded hardware testing capability: defining the methodology for hardware and firmware assessments, developing the tooling and frameworks the team uses, and driving new approaches to hardware-focused security testing. CyberCX research publications byline him as a Senior Security Consultant.
Across his career he has performed hundreds of penetration tests and technical security assessments for organisations in education, finance, banking, healthcare, utilities, telecommunications and government. The work includes hardware and firmware penetration testing and reviews, network segmentation testing, firewall assessments, vulnerability assessments, and web and web-service penetration testing, as well as in-depth reviews of PCI DSS environments, cloud platforms and enterprise infrastructure.
His research interests sit at the boundary of hardware and software: pulling apart embedded devices, analysing firmware, reverse engineering undocumented interfaces and developing proof-of-concept exploits so that vendors can fix the underlying flaws. The public record of that work is summarised below, with links to the original advisories.
Selected original research
These summaries follow the wording of the primary advisory in each case. Where an issue needs local or physical access rather than network access, that is stated, because secondary reporting has sometimes overstated it.
NetComm industrial router and VDSL modem remote code execution (2024)
In 2024 CyberCX published two pieces of research by Chris into NetComm devices sold into Australian industrial and consumer markets. The NetComm NTC-221 industrial IoT router contained an unauthenticated remote code execution flaw in its web interface that gave an adversary a root shell without credentials; NetComm released firmware 2.1.36.0 to address it. The NetComm NL1901ACV VDSL modem contained an input-sanitisation flaw that allowed authenticated remote code execution as root, fixed in firmware R6B033. Both posts document the discovery, the vendor coordination and the fix versions.
Cisco IOS XR bootloader information disclosure (2023)
Cisco advisory, credited to "Chris Watts of CyberCX". CVE-2023-20064.
Cisco's advisory describes a weakness in the GRUB bootloader of IOS XR Software, which runs on ASR 9000, NCS and related carrier routers. An attacker connected to the console port while the device is power-cycled could read sensitive files through the bootloader command line. This is a physical-access issue, not a remote exploit, and Cisco rated it medium severity.
The most serious of these was a buffer overflow in the web server of nine Cisco DOCSIS 3.0 cable modem and gateway models (DPC and EPC 3010, 3212, 3825 and 3925, and the DPQ3925), allowing an unauthenticated remote attacker to execute arbitrary code. Cisco published it in July 2014 with its highest base score, and SecurityWeek and Threatpost reported it that week, naming Chris as the reporter. A similar unauthenticated remote code execution flaw in the DPC2203 and EPC2203 cable modems followed in March 2016. Three further findings in the DPQ3925 wireless residential gateway covered cross-site request forgery, information disclosure through the HTTP server, and a denial-of-service condition that restarts the device.
Chris reported six issues in the Cisco SPA300 and SPA500 series desk phones used by small businesses. The best known, published in March 2015, allowed an unauthenticated attacker with network access to send a crafted XML request to a phone in its default configuration and listen to its audio stream or place calls from it. Cisco credited "Chris Watts of Tech Analysis", and the finding was covered by iTnews, The Register, SecurityWeek, The Hacker News and Tripwire. The earlier July 2014 notices described a cross-site scripting flaw in the phone's web interface and an authentication weakness in the debug console that gives local shell access; Cisco's current notices for those two do not display a researcher credit, and the attribution rests on contemporary reporting by iTnews. Later advisories covered a firmware image upload weakness that requires local shell access, an HTTP denial of service, and a cross-site request forgery flaw.
Every record below links to the primary advisory or publication. "Credit" quotes the attribution wording as currently published by the vendor or publisher; where the vendor page carries no name, the attribution source is given instead. Dates are the advisory's own first-published dates. Severity scores are omitted because vendor, NVD and CISA scores for several of these records differ in version and value; the linked advisories carry the vendor's scoring.
Vulnerability reports credited to Chris Watts, newest first
CVE
Vendor and product
Issue
Access needed
Published
Credit
Source
CVE-2024-26519
NetComm NTC-221 industrial IoT router
Unauthenticated remote code execution
Unauthenticated access to the web interface; code runs as root.
Author. Published by Chris Watts, Security Testing and Assurance; credit line "Chris Watts – CyberCX"
"Cisco would like to thank security researcher Chris Watts for discovering and reporting this vulnerability." (Cisco advisory, Source section (no organisation named))
Unauthenticated local attacker with access to the device shell. Not remote code execution.
"Cisco would like to thank security researcher Chris Watts for discovering and reporting this vulnerability." (Cisco advisory, Source section (no organisation named))
Unauthenticated remote attacker; a user must click a crafted URL.
The currently published Cisco notice displays no named credit. Attribution to Chris Watts of Tech Analysis is reported by iTnews (22 March 2015). Source.
Debug console authentication weakness, local code execution
Unauthenticated local attacker with local access to the device. Not remote.
The currently published Cisco notice displays no named credit. Attribution to Chris Watts of Tech Analysis is reported by iTnews (22 March 2015). Source.
This index lists public records with named attribution. It is not a count of all vulnerabilities Chris has reported; findings disclosed privately to vendors or clients are not included.
Independent coverage
Articles by journalists and industry writers that name Chris Watts in connection with the research above. Several articles report the same discovery, so they are grouped by the research they cover; the number of articles is not the number of discoveries.
July 2014: Cisco cable modem and gateway remote code execution (CVE-2014-3306)
Reports Cisco's advisory for the web-server buffer overflow in nine cable modem and gateway models and names Chris Watts of Tech Analysis as the reporter.
The original interview. Quotes Chris on the severity of the flaw and connects it with the two 2014 phone vulnerabilities; most of the following day's coverage cites this article.
Security vendor blog post that names Chris as the discoverer of the three phone vulnerabilities and links to the Tech Analysis research page preserved on this site. Byline not captured in the archived copy.
Attributes the DPQ3925 denial of service and the DPC2203/EPC2203 remote code execution to Chris; the same article covers a separate gateway flaw credited to Kyle Lovett, which is not Chris's.
Security news blog report of the March 2016 advisories, again distinguishing Chris's two findings from Kyle Lovett's.
Engineering and other projects
VCM1250 parcel measuring instrument
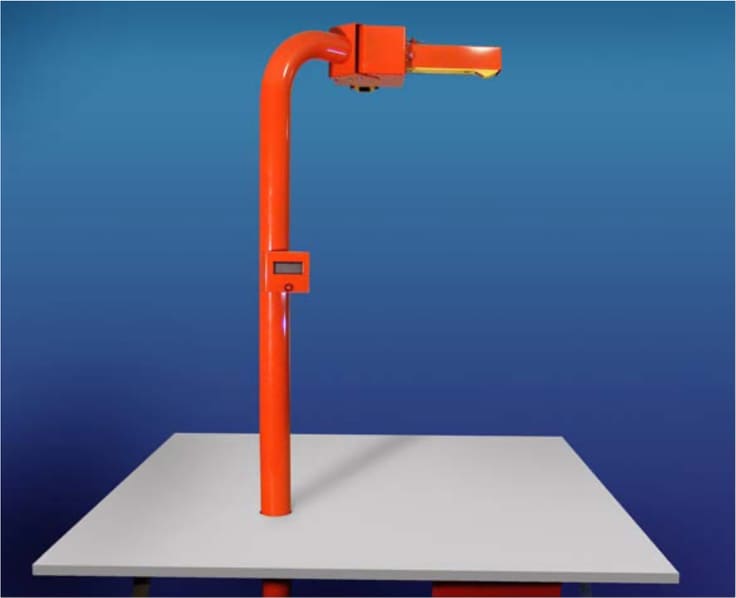
The VCM1250 non-contact dimensional measuring instrument. Photograph supplied by Chris Watts.
CubeLogic Systems came to Tech Analysis with a problem: they needed a non-contact machine that could measure postal parcels for trade. Chris designed and built the VCM1250 for them. A parcel placed on its platform is scanned by laser profile sensors, and the instrument reports length, width, height and volume in real time, on screen and over Ethernet and serial connections. He then took it through pattern approval under Australia's trade measurement framework: the National Measurement Institute issued certificate of approval NMI 13/1/28 for the CubeLogic Systems VCM1250 on 19 August 2015, covering objects from 10 to 59 centimetres on each side. The certificate is a record about the instrument, issued to the client company; it does not name individuals, and Chris's design and build role is his own account.
Chris co-founded PageLeap with his friend Will Pemble and served as its chief technology officer; the company's About page lists "Will Pemble, CEO and Co-Founder" and "Chris Watts, CTO and Co-Founder", describing him as a cyber security expert, embedded hardware specialist and full-stack developer. PageLeap built a platform for fast-loading landing pages. Its homepage now states that PageLeap has ended and that "the technology and patents were acquired in a private transaction"; the purchaser, price and date have not been published. Will Pemble discussed building PageLeap with his partner Chris in a 2024 interview on The CTO Show with Mehmet.
Chris founded Wonderland History, a website dedicated to the remembrance and history of Australia's Wonderland, also known as Wonderland Sydney, the amusement park at Eastern Creek in western Sydney that opened in December 1985 and closed in April 2004. The site describes itself as keeping the memory of the park alive since 2004, beginning as a record of the park's demolition, and has grown into a large archive of photographs, documents, maps and ride histories contributed by former staff and visitors; archived copies of the site go back to 2006. A 2012 press release on the site names Chris as its founder, Wikipedia's article on the park cites the site repeatedly, and a 2017 BuzzFeed photo feature on the abandoned park credits Chris Watts for its photographs and the online community he and friends built around it. Chris also set up and, with a small team of helpers, runs the public Facebook group Australia's Wonderland History, which has grown past 25,000 members.
A selected account. Roles overlapped at times; Tech Analysis ran alongside employed positions. Dates for the earlier roles are from Chris's own records.
November 2020 to present
CyberCX: Senior Cybersecurity Consultant; Embedded Systems Service Lead and Subject Matter Expert, Security Testing and Assurance
Hardware, firmware, network, cloud and application penetration testing across education, finance, banking, healthcare, utilities, telecommunications and government. Leads the embedded hardware testing capability: methodology, tooling frameworks and new assessment approaches. Credited reporter of CVE-2023-20064 (Cisco) and author of the 2024 NetComm research.
2018 to 2020
Servers Australia: Senior Systems Engineer
Virtualisation lead for private-cloud and VPS products, national infrastructure automation and auditing, network backup tooling, migrations and high-availability firewall systems.
May 2010 to January 2026
Tech Analysis: Founder and owner
Australian-owned technology consultancy: security testing and vulnerability research (including the zero-day findings reported to Cisco), custom software and firmware in C, C++, assembly and other languages, Linux kernel modules and device drivers, systems administration across Linux, AIX, BSD, Solaris and VMware, network engineering, data recovery, migrations, hosting and web development, for clients from startups to listed companies. Source of the Cisco credits to "Chris Watts of Tech Analysis" between 2014 and 2017. Closed in January 2026.
2006 to 2010
Sony DADC: Network Systems Engineer
Network and server engineering for a manufacturing and distribution business: security audits and assessments, patching, segregated security and building-management networks, VoIP, storage and fibre networking, including a long-distance dark-fibre wavelength-division multiplexing link and enterprise AIX, Linux, Windows, Mac and VMware systems.
2000 to 2006
Web1: Co-owner
Web, mail and DNS hosting, ISP-related services, programming and web development, and deployments and migrations of healthcare practice systems.
1996 to 1999
Self-employed: IT consultant
Small-business consulting, building and servicing computers, and Apple and PC repairs.
1995
Status Graph: Apple Service Engineer
Servicing 68k Macintosh and Power Macintosh systems.
1992 to 1995
CGL Software: Programmer
68k Apple Macintosh software development in Think C and C++.
Technical background
Chris programs in C and C++, assembly across several instruction sets, PHP, JavaScript, shell and Python. He has written Linux kernel modules and device drivers, firmware and other embedded code, and has long experience with network design and administration (Cisco, Juniper, Brocade and others), virtualisation and cloud infrastructure, and Unix, Linux, Windows and Mac systems. On the hardware side he does electronics fault-finding, board-level repair and PCB design. That mix is what makes embedded device security a natural specialty: he can read the schematic, the firmware and the network traffic.
Professional enquiries about security testing should go to CyberCX.
About Tech Analysis. Tech Analysis is no longer trading. This website is maintained as the personal profile and research archive of its founder, Chris Watts, who now works at CyberCX. Earlier research remains attributed to Tech Analysis as originally published.
Chris Watts is a common name. This page concerns the Australian security researcher associated with Tech Analysis, CyberCX, PageLeap and Wonderland History, and is not connected with other people who share the name.